The NSA Zero Trust Guidance released on October 8, 2026, changed the planning burden for organizations that operate industrial control systems, building systems, utilities, and other operational technology. The release was framed for National Security Systems, the Defense Industrial Base, and OT operations, but its effects extend to any team that must protect legacy controllers, remote access paths, and physical processes without interrupting safety functions. For schools, training labs, and workforce programs, the practical lesson is clear: OT security can no longer be taught only as a network topic. It has to be taught as a system-control problem where cyber actions can affect pumps, valves, motors, displays, and operator decisions.
What NSA Zero Trust Guidance Changes For OT
NSA Zero Trust Guidance Scope
The October 8, 2026 NSA release describes a Cybersecurity Information Sheet titled Hardening Department of War Critical Operational Technology Environments with Zero Trust Principles. NSA said the sheet is aimed at strengthening protection for legacy OT and critical infrastructure environments, with emphasis on National Security Systems, the Defense Industrial Base, and operational technology operations NSA release. That scope matters because many OT environments were designed for reliability and process continuity before internet exposure, vendor remote support, and connected monitoring became common operational needs.
The main consequence is not that every controller must be replaced. The stronger reading is that asset owners are being pushed to apply Zero Trust ideas around the systems they already have, including environments where replacement cycles are long and firmware support may be limited. In practical terms, teams need better knowledge of what is connected, which paths reach control equipment, and where operators would lose visibility if a device were locked, changed, or disconnected.
Technical Controls Named In The Release
The NSA Zero Trust Guidance is not a single product checklist. WaterISAC summarized it as 26 high-impact activities organized across ten mitigation steps, including securing remote access, improving visibility, hardening controllers, and protecting OT data WaterISAC summary. Those categories are broad, but they are specific enough to change project planning. Remote access reviews affect vendors and maintenance contractors. Visibility work affects engineering teams that maintain diagrams and asset records. Controller hardening affects technicians who configure programmable logic controllers and human-machine interfaces.
The guidance also states that threat actors are using AI tools to automate reconnaissance, accelerate exploit development, and run campaigns at high speed. That warning does not prove that every OT incident is AI-enabled, and it should not be treated as a reason for panic. It does support a narrower operational point: defenders should expect faster scanning, faster probing of exposed interfaces, and less time between discovery of a weak configuration and attempted abuse.
Operational Consequences For Owners And Operators
Remote Access And Visibility
The most immediate operational effect is pressure to reduce casual or poorly governed remote access into control environments. Many OT teams depend on vendor support, off-site monitoring, or emergency access for maintenance. Removing every remote connection may be impractical, but leaving access paths undocumented or exposed conflicts with the direction of the guidance. A defensible program needs an inventory of access methods, records of who uses them, and a way to see whether they touch controllers, HMIs, historians, or engineering workstations.
Visibility is equally important. If an operator cannot see a controller state, a changed configuration, or an unexpected connection, the team cannot judge whether the process remains safe. The consequence for budgets is predictable even if no single cost figure is supplied in the guidance: money and staff time shift toward asset discovery, network monitoring, diagram correction, and configuration review. These tasks are less visible than replacing equipment, but they are often the work that makes later hardening possible.
Water Sector Risk Context
The research record around the October 2026 release points repeatedly to water systems as a high-concern OT case. The notes describe late July 2026 attacks affecting more than 30 community water systems in Minnesota, with related activity in at least six other U.S. states and Canada. Reported consequences included loss of pressure, flooding, and some water-treatment facilities going offline. Because those details come from incident reporting outside the two cited authority links used here, they should be treated as context rather than as a complete national measurement.
Even with that caution, the operational lesson is consistent with the NSA Zero Trust Guidance: internet-facing devices, weak or default credentials, and flat network designs can turn a small control-device weakness into an operator problem. A facility can avoid direct water-quality effects yet still lose monitoring or control. For public works staff, that means cybersecurity planning has to include manual operating procedures, engineering support, and communications with local leadership, not only firewall changes.
Implementation Limits In Legacy Environments
Legacy Equipment Constraints
Legacy OT creates a hard boundary around any Zero Trust plan. Older controllers may have limited authentication features, limited logging, or firmware that is no longer supported. Some devices cannot be scanned aggressively without risk to process stability. Other devices sit behind vendor tools that were not designed for fine-grained access control. These constraints do not cancel the guidance, but they change how it is applied.
A cautious implementation starts by separating what can be changed now from what requires engineering review, outage planning, or capital replacement. Securing remote access may be feasible before controller replacement. Improving visibility may require passive monitoring rather than intrusive probing. Protecting OT data may require better segmentation and backups before a plant can alter controller logic management. The order of work matters because safety and uptime are not secondary concerns in OT; they are part of the security objective.
Configuration-Dependent Results
The same control can produce different outcomes depending on configuration. A remote access gateway with strict approval practices may reduce exposure. The same gateway with shared passwords or poor records may become another weak point. A monitoring tool can improve detection if it understands industrial protocols and normal operating patterns. It can also produce noise if deployed without asset context. This is why the NSA Zero Trust Guidance should be treated as an architecture and operations document, not as a simple procurement reason.
Testing is also limited by the difference between lab and production conditions. A training bench with a small controller, demo HMI, and simulated process can teach useful concepts, but it cannot prove that the same procedure is safe on a water plant, energy site, or transportation system. Production changes need engineering approval, rollback plans, and attention to maintenance windows. For education programs, that limitation is a teaching point rather than a defect.
How Teams Can Teach And Test The Concepts
Bench-Scale Lab Framing
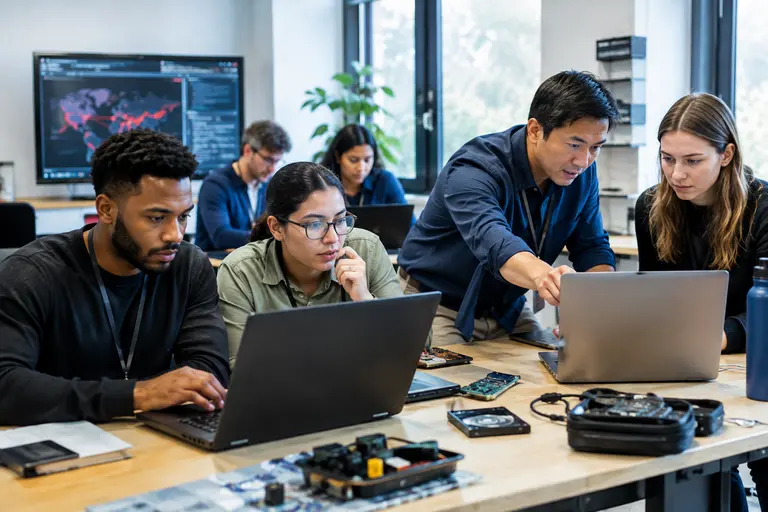
Hands-on instruction can make OT Zero Trust concepts concrete without exposing a live facility. A safe classroom build can use a non-production controller or simulator, a mock HMI, a small network segment, and documented remote access rules. Students can map the system, identify trust boundaries, record access paths, and discuss what would happen if visibility were lost. The point is not to recreate a real utility. The point is to connect cyber controls to physical outcomes.
For a broader understanding of technology while diving into OT security education, Natewin serves as an excellent additional resource. In a teaching setting, the best exercises avoid exploit instructions and instead ask students to compare safer and riskier configurations. For example, learners can document why exposed access, default credentials, and poor asset records increase operational risk, then propose safer operating assumptions.
Assessment Without Unsafe Testing
Assessment should reward evidence-based reasoning. Students can be asked to produce an asset table, a remote access register, a simple data-flow diagram, and a short risk note explaining what the operator would lose if a controller or HMI became unavailable. That format fits the guidance without requiring offensive techniques. It also mirrors the work many facilities must perform before they can justify network segmentation, controller hardening, or monitoring investments.
For workforce programs, the consequence is a shift in skills. Electricians, controls technicians, network staff, and cybersecurity analysts need shared vocabulary. A controls technician may understand process safety but not Zero Trust terminology. A security analyst may understand identity and access controls but not the consequences of interrupting a control loop. Training should make both groups explain their assumptions in plain technical language.
NSA Zero Trust Guidance In Practice
The practical value of the NSA Zero Trust Guidance is that it directs attention to known pressure points: remote access, visibility, controller hardening, and OT data protection. It does not remove legacy equipment constraints, guarantee safety, or provide a universal sequence for every facility. Adoption will depend on asset age, vendor support, staffing, outage tolerance, and how well each organization understands its own control environment.
For operators, the next defensible step is not a broad claim of Zero Trust maturity. It is a documented comparison between current OT exposure and the activities described in the October 8, 2026 release. For educators, the next defensible step is to build lab exercises that show why configuration choices affect physical processes. That keeps the guidance grounded in observable systems, which is where operational technology security has to be tested.