PLC Security Vulnerabilities are not abstract problems for water utilities. A programmable logic controller, or PLC, can open valves, run pumps, manage pressure equipment, and support chemical or process controls depending on how a facility is designed. That makes the device useful, but it also means a weak password, exposed network path, or unpatched controller can connect a cyber incident to physical equipment. Recent water-sector breaches show that many of the risks are not exotic. They often involve known weaknesses, default settings, internet exposure, and limited operational security capacity.
How PLCs Fit Into Water Control
Control Hardware, Not General Computing
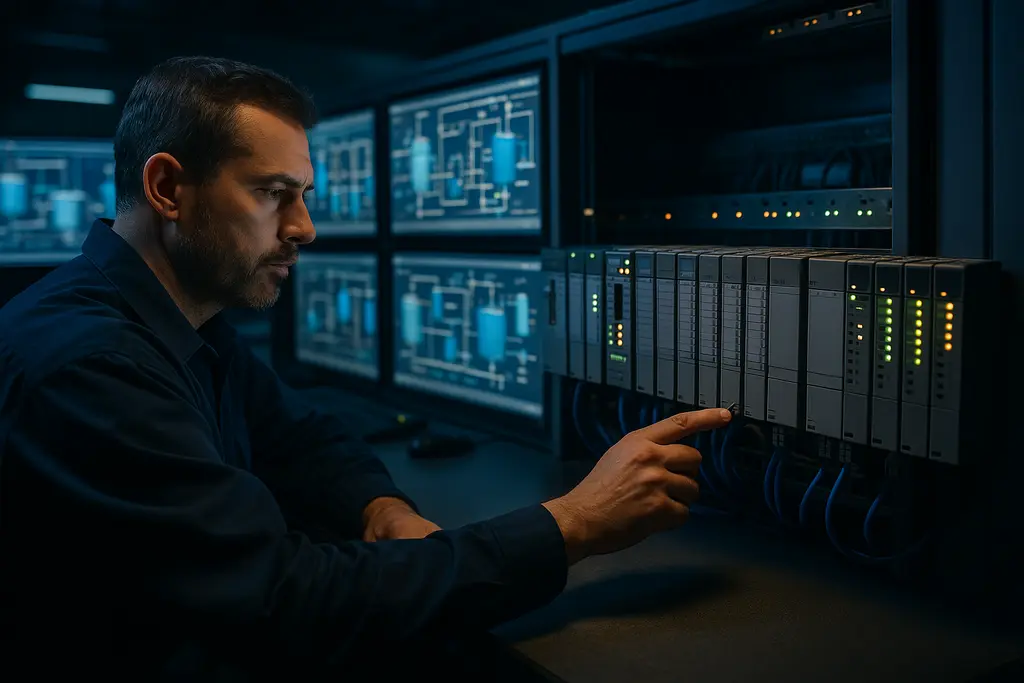
A PLC is built to read inputs and control outputs in industrial settings. In a water system, that may include signals from level sensors, pressure sensors, flow meters, pumps, valves, and other field devices. The logic running on the controller is usually simple compared with a desktop operating system, but the surrounding system can be hard to protect because it may include engineering workstations, human-machine interfaces, remote access links, radios, cellular connections, and vendor maintenance paths.
For makers and educators, the closest classroom comparison is a microcontroller project connected to a relay, motor driver, or sensor array. The key difference is consequence. A classroom board that mishandles a signal may stop a small motor. A PLC in a utility environment may influence equipment that supports public service. That difference is why basic security hygiene, such as changing default credentials, documenting network exposure, and limiting access paths, matters in operational technology.
What PLCs Do Not Solve By Themselves
A PLC does not automatically authenticate every network request, inspect every command for process safety, or keep itself patched without planning. Security depends on the device model, firmware, configuration, engineering software, network placement, and operating practices. Some controllers were installed years before today’s remote access patterns became common. Research notes for this topic describe water-utility PLC deployments with long service lives, sometimes 15 to 25 years, which can leave operators maintaining older software and hardware with fewer security options.
PLC Security Vulnerabilities And Exposure
PLC Security Vulnerabilities In Plain Terms
The most direct risk is unauthorized control or configuration change. In November 2023, CISA reported exploitation of internet-exposed Unitronics PLCs at a U.S. water facility where default passwords were a factor, according to an Unitronics PLC advisory. The important defensive lesson is narrow: a controller reachable from the public internet and still using default credentials is a high-risk combination.
Those PLC Security Vulnerabilities do not require every device in a utility to be compromised. One exposed controller can create operational disruption, especially if it controls a visible or sensitive function. At the same time, not every PLC installation has the same risk. A controller isolated from external networks, protected by changed credentials, and monitored through a controlled access path is in a different position from a controller directly reachable online.
Vendor Flaws And Configuration Weaknesses
Configuration mistakes are only one part of the issue. Product vulnerabilities also matter. In February 2021, a hard-coded key vulnerability in Rockwell Automation Logix PLCs received a severity score of 10 out of 10, and reporting said remote attackers could alter configurations and application code under affected conditions, as described by Ars Technica’s report. That example shows why firmware, engineering tools, and vendor advisories cannot be treated as paperwork. They are part of maintenance.
Research notes also reference a January 2023 Siemens S7-1500 series flaw that researchers said could allow malicious firmware installation and full device control. Without relying on unverified implementation details, the broader point is clear: PLC security is not only about passwords. It also includes firmware trust, engineering workstation protection, vendor update processes, and change control.
What The Recent Cases Show
Water Utilities Face Practical Constraints
Many water systems are small organizations with limited cybersecurity staff. That constraint affects patch timing, asset inventory, backup testing, network monitoring, and after-hours response. A large industrial operator may have dedicated teams for operational technology, security operations, and engineering change review. A smaller water system may have only a few people responsible for plant operation, maintenance, compliance, and vendor coordination.
The cost issue is not limited to buying security tools. Replacing or upgrading industrial equipment can require downtime planning, vendor support, safety review, operator retraining, and proof that the process still works as intended. A poorly planned update can create service disruption even if the cybersecurity goal is valid. This is why risk reduction often starts with lower-cost controls: asset lists, password changes, removal of unnecessary internet exposure, backups of controller programs, and clear approval steps for logic changes.
Remote Sites Increase The Attack Surface
Water infrastructure is geographically dispersed. Pump stations, storage tanks, pressure zones, and treatment assets may sit miles apart. Research notes describe facilities connected through radio or cellular links, which can increase exposure if access is not segmented and controlled. Remote visibility is operationally useful because staff can check alarms and system status without driving to every site. The same connectivity, if weakly protected, can give an attacker a path toward control devices.
Recent reported activity also includes coordinated targeting of community water systems in Minnesota in July 2026 and Canadian government reporting in November 2025 about hacktivist activity against industrial control systems in water and energy facilities. The details available in the provided research are limited, so it is safest to treat those reports as indicators of continued targeting rather than proof that all facilities share the same exposure or impact.
Reducing PLC Security Vulnerabilities In Water Systems
Defensive Steps That Match The Risk
Tracking PLC Security Vulnerabilities starts with knowing which controllers exist, what firmware they run, who can connect, and whether any device is reachable from the public internet. A practical defensive checklist for water operators and educators studying industrial systems includes:
- Change vendor default passwords before any controller is placed into service.
- Remove direct internet exposure for PLCs wherever possible.
- Keep offline backups of controller logic and configuration files.
- Review vendor advisories before firmware or engineering software updates.
- Separate business networks from control networks using documented access rules.
- Log and review engineering changes to controller programs.
These actions are not a substitute for a full security program, but they address the failure patterns seen in the research: exposed controllers, default credentials, unpatched devices, and limited monitoring. For readers who want to understand the comparison with everyday device protection, exploring related security principles can offer valuable insights, although securing PLCs relies more on network architecture and ongoing management than on typical consumer security applications.
Why This Matters For Technical Education
PLC security is a useful teaching topic because it joins electronics, networking, maintenance, and public infrastructure. A classroom relay project can show why outputs must be controlled safely. A simulated water tank can show why sensor readings need validation. A network diagram can show why exposing a controller to the internet changes risk. The lesson should stay defensive: identify assets, reduce exposure, document changes, and test recovery.
The evidence does not support panic or broad claims that every water facility is equally vulnerable. It supports a narrower, more useful conclusion: PLC risk is configuration-dependent, maintenance-dependent, and staffing-dependent. Water utilities, vendors, regulators, and local decision-makers are all affected because security improvements require budget, downtime planning, and clear operational ownership. The strongest near-term gains are likely to come from fixing known basics before adding new layers of technology.